

Inside the Fraud Lab: From Leaked Data to Identity Fraud
Tuesday, October 27 at 11 AM EDT / 4 PM CET
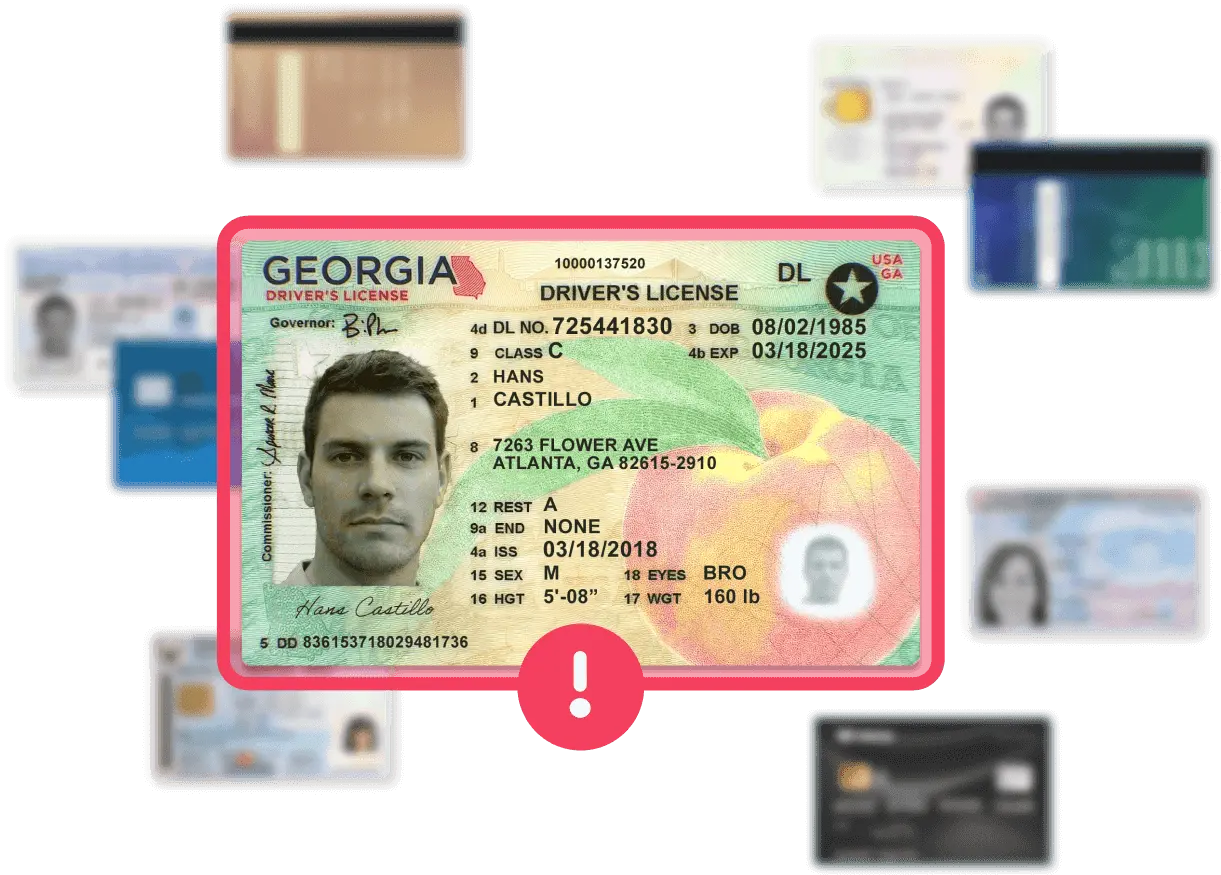
Recent reports of exposed identity documents and personal data raise a pressing question: what can fraudsters do with that information—and what does it take to stop them?
Join Microblink’s Fraud Lab as they trace the path from leaked identity data to the attacks it can enable and the defenses built to detect them.
Through real-world examples, we’ll explore how attackers exploit exposed information, where biometric checks and injection attack detection come into play, and how the team investigates fraud it hasn’t seen before. We’ll also look at the challenge of turning a newly discovered attack into a defense that works across different document types.
Key takeaways:
- How exposed identity documents and personal data can enable different types of fraud
- The role of biometric checks and injection attack detection in defending against those attacks
- How Fraud Lab investigates unfamiliar fraud and develops defenses that work across document types
You’ll hear from:
- Hristina Nedyalkova, Data Engineer, Microblink
- Vincenzo D’Elia, Engineering Director, Microblink
- Radu Tudoran, VP of Engineering, Microblink
You're in!
Thanks for registering. Look out for your registration confirmation and calendar invite, we'll send it to the email you registered with.