Continuous Identity Verification: Stop Account Takeover and Synthetic Identity Fraud

Identity fraud doesn’t happen at a single moment anymore.
It happens across sessions, across devices, across time. A user can pass onboarding legitimately and still become a risk hours, days, or months later through account takeover, synthetic identity evolution, or credential compromise. Account takeover (ATO) fraud occurs when an attacker gains unauthorized access to a legitimate user’s account and uses that access for fraudulent purposes. Depending on the account, an attacker may change personal information, redirect payments, make unauthorized purchases or transfers, access sensitive data, redeem rewards, or use the trusted account to commit additional fraud.
That’s why organizations are shifting from one-time verification to continuous identity verification; a model that evaluates identity not as a checkpoint, but as an ongoing process.
How do account takeover attacks happen?
Attackers have several ways to obtain the credentials or access needed to take over an account. Phishing and social engineering remain common entry points, with attackers impersonating trusted companies, employees, financial institutions, or other individuals to persuade users to reveal passwords, authentication codes, or other sensitive information. These attacks can also take the form of smishing through text messages or vishing through phone calls.
Why One-Time Verification No Longer Works
Traditional identity systems were built around static events such as onboarding, login, or high-risk transactions. Once a user passed those checks, they were often trusted indefinitely.
That model breaks in today’s environment. Fraudsters now:
- Take over legitimate accounts after onboarding
- Build synthetic identities that evolve over time
- Use AI to mimic real users across sessions
The result is a dangerous gap between initial verification and ongoing trust. Continuous identity verification closes that gap by ensuring identity is never assumed, it’s always validated.
How can businesses prevent account takeover fraud?
Strong authentication is an important starting point. Multi-factor authentication (MFA) and two-factor authentication (2FA) make a stolen password less useful by requiring another form of authentication. Organizations can further reduce exposure to phishing by adopting phishing-resistant authentication methods such as passkeys and FIDO2-based credentials, which reduce reliance on passwords and authentication secrets that users can inadvertently provide to an attacker.
Authentication alone, however, cannot address every form of account takeover. Organizations should combine it with risk signals that help determine whether activity remains consistent with the legitimate user. Device information, behavioral patterns, transaction history, location and network signals, changes to account information, and other contextual data can help identify risk throughout the account lifecycle.
Rather than challenging every user at every interaction, businesses can use these signals to trigger step-up authentication when risk increases, creating additional friction where it is warranted while allowing trusted users to continue normally.
How Continuous Identity Verification Works Across the User Journey
Continuous identity verification operates by layering signals and evaluating them in real time across every interaction.
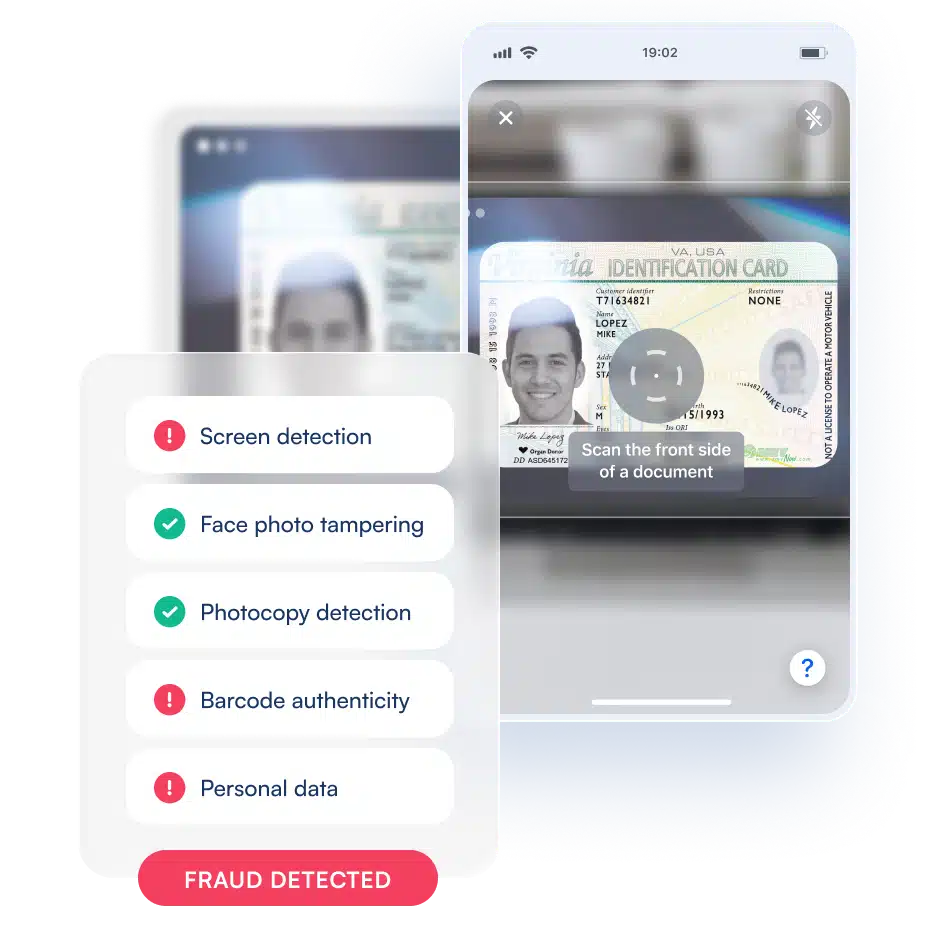
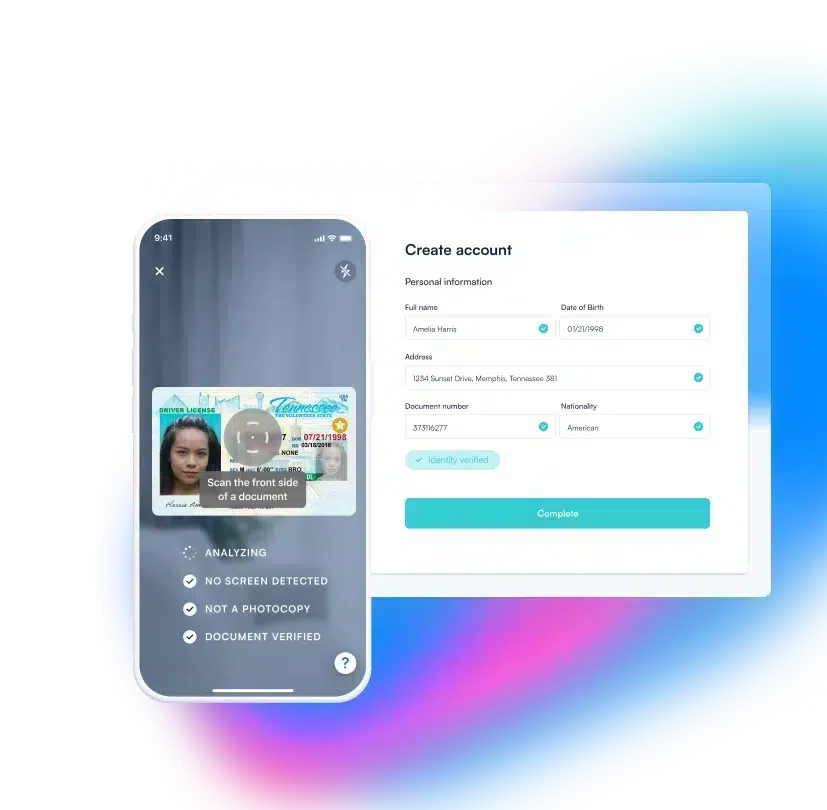
During onboarding, identity is established through document verification and biometric matching. But instead of stopping there, the system continues to monitor identity during logins, transactions, and account changes. Behavioral patterns, device signals, and contextual data are analyzed continuously to ensure the same trusted identity is still present.
If something changes, like unusual behavior, a new device, or inconsistent location, the system can trigger step-up authentication or block activity altogether. This transforms identity verification from a static gate into a dynamic control system.
Key Capabilities of Continuous Identity Verification
A robust continuous identity verification system combines multiple layers of intelligence working together:
- Real-time behavioral monitoring to detect anomalies in how users interact
- Device intelligence and binding to ensure trusted environments
- Biometric verification including liveness detection and face matching
- Contextual risk analysis based on location, velocity, and usage patterns
- Adaptive authentication that escalates verification only when needed
- Continuous authorization to validate actions, not just identities
These capabilities work together to create a living identity profile that evolves with the user and flags risk as it appears.
Continuous vs. Traditional Identity Verification
| Capability | Traditional Verification | Continuous Identity Verification |
|---|---|---|
| Timing | One-time (onboarding/login) | Ongoing across lifecycle |
| Risk Detection | Static, point-in-time | Real-time, evolving |
| Fraud Coverage | Limited to entry points | Covers account takeover, session fraud, synthetic identities |
| User Experience | Often high friction upfront | Low friction, adaptive |
| Decisioning | Binary (pass/fail) | Dynamic, risk-based |
Balancing Security and User Experience
One of the biggest misconceptions about continuous identity verification is that it increases friction. In reality, it often reduces it.
By continuously monitoring risk in the background, organizations can allow the majority of legitimate users to move seamlessly through their journey without interruption. Only high-risk scenarios trigger additional checks.
This creates a system where security is stronger and the experience is smoother, because friction is applied precisely where it’s needed, not everywhere.
Regulatory and Compliance Considerations
Continuous identity verification aligns closely with evolving regulatory expectations, particularly in KYC and AML frameworks that increasingly emphasize ongoing monitoring rather than one-time checks.
Regulators are no longer satisfied with initial verification alone. They expect organizations to:
- Monitor user activity over time
- Detect suspicious behavior in real time
- Maintain audit trails of identity-related decisions
A continuous model supports these requirements by providing ongoing visibility, traceability, and control across the customer lifecycle.
What should you do after an account takeover?
Detection should trigger a defined incident-response process rather than simply blocking an individual transaction. Depending on the nature of the compromise, organizations may need to temporarily restrict the account, revoke active sessions and authentication tokens, reset credentials, investigate recent account changes and transactions, and require the legitimate customer to re-establish control of the account.
Teams should also preserve relevant evidence and determine how the takeover occurred. Understanding whether the initial compromise involved phishing, credential stuffing, malware, session theft, or another attack can help prevent the same method from succeeding again. Where financial loss or criminal activity has occurred, appropriate internal escalation and regulatory or law-enforcement reporting requirements may also apply.
How Microblink Enables Continuous Identity Verification
Microblink’s Identity Intelligence OS is built around the idea that identity is not a moment, it’s a continuum.
It combines document verification, biometrics, device intelligence, and behavioral signals into a unified system that continuously evaluates identity across the entire user journey. By enabling real-time decisioning and adaptive workflows, Microblink helps organizations reduce fraud, improve conversion, and maintain compliance without adding friction.
Rather than relying on static checks, it provides continuous identity control, ensuring that trust is constantly validated—not assumed.
Identity Is No Longer a Checkpoint
Fraud is continuous. Identity verification needs to be as well.
Organizations that rely on one-time verification are operating with blind spots that fraudsters are increasingly exploiting. Continuous identity verification removes those blind spots by turning identity into a real-time, always-on system of control.