The Complete Guide to Identity Verification APIs

As businesses and transactions migrate online, securing identity data has moved from a nice-to-have to a must-have. Not having a proper identity verification process in place can have a significant financial impact and result in fines. This is because it can lead to fraud and money laundering, which are serious crimes that can harm businesses and society as a whole. This isn’t just about keeping out the bad actors—it’s about fostering trust, facilitating user engagement, and complying with a growing list of regulations.
But how can you do that without putting your user experience at risk?
Here’s your complete guide so you can unlock this tool’s powers.
What is an API for identity verification?
An Identity Verification API is a structured interface that allows your application to communicate with an external identity verification service. Unlike a generic API, an identity-specific API is purpose-built to handle sensitive personal data—connecting your platform to document scanning engines, biometric matching systems, liveness detection modules, and authoritative identity databases.
In practical terms, when a user submits their ID document or biometric data through your application, the API transmits that data to the verification service, processes it through a series of automated checks, and returns a structured result—such as a pass/fail decision, confidence score, or list of flagged fields—back to your system in real time.
This means you don’t need to build document recognition, fraud detection, or compliance logic from scratch. The API handles the complexity, and your application simply sends a request and acts on the response.
How does an Identity Verification API differ from manual identity verification?
Manual identity verification requires a human reviewer to inspect documents, cross-check information, and make a judgment call. This approach is slow, inconsistent, and difficult to scale. A single reviewer can process only a limited number of verifications per day, and human error introduces risk at every step.
An Identity Verification API automates this entire workflow:
| Factor | Manual Verification | Identity Verification API |
|---|---|---|
| Speed | Minutes to days | Seconds |
| Scalability | Limited by headcount | Scales on demand |
| Consistency | Subject to human error | Standardized, rule-based |
| Cost | High per-verification labor cost | Lower marginal cost at scale |
| Compliance | Difficult to audit | Automated audit trails |
| Availability | Business hours only | 24/7 |
For businesses processing high volumes of users—or operating across multiple time zones—the operational and financial case for API-based verification is clear.
How is identity verification done?
Verifying someone’s identity online may seem straightforward, but there’s quite a bit going on under the hood. Let’s break down this process into clear steps.
The process behind an Identity Verification API
A secure and easy remote ID process involves a few steps, including document verification, biometric scans, and data validation. These steps ensure the person trying to access the system is who they say they are.
Step 1: Image capture
First things first—image capture. Whether it’s identity documents or biometric data, this step lays the groundwork for the entire process. A good system can help make the best first impression by being user-friendly and quick, minimizing the risk of user drop-offs, and maximizing engagement.
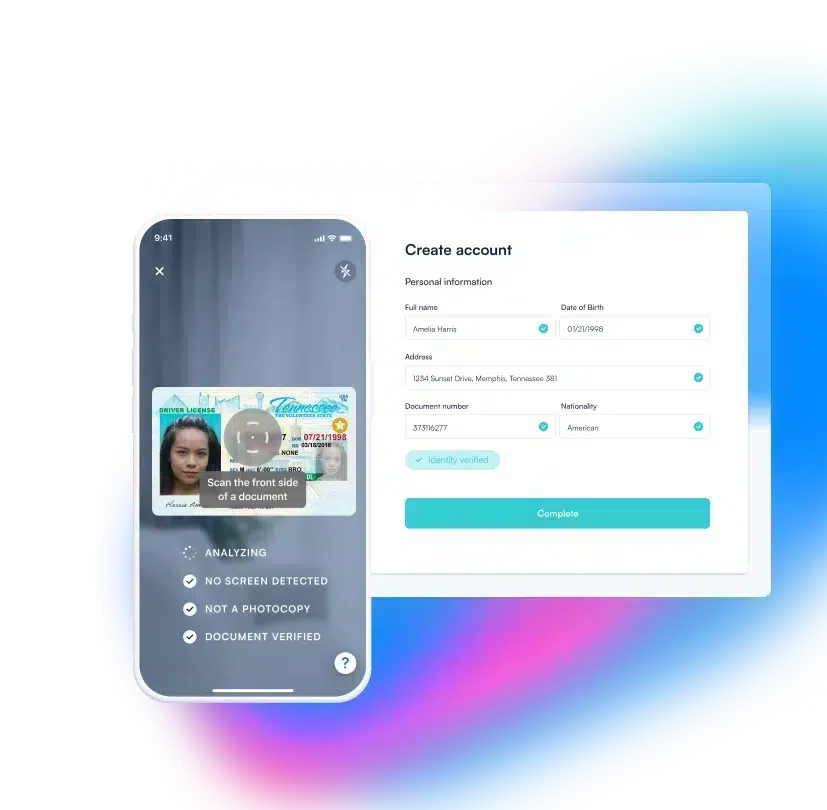
Take BlinkID Capture, for instance. AI-powered ID scanning software allows you to acquire high-quality document images automatically without glare, blur, or obstructions.

Step 2: Liveness detection and data extraction
Before moving on to data extraction, liveness detection comes into play to ensure the user is a real, live human being. Users may be prompted to perform simple actions like blinking or turning their head, confirming their live presence and guarding against spoofing attacks using photos or pre-recorded video.
Once the image is captured, the system automatically extracts relevant information using Optical Character Recognition (OCR) and machine learning models. The technology identifies specific fields—name, date of birth, document number, expiration date, and more—and pulls them out for verification. Automating this process eliminates human error and saves time, streamlining the experience for both the business and the user.
OCR accuracy is a critical evaluation criterion when selecting a provider. Leading solutions achieve accuracy rates above 99% on supported document types, significantly reducing the need for manual review fallback.

Step 3: Data verification and fraud checks
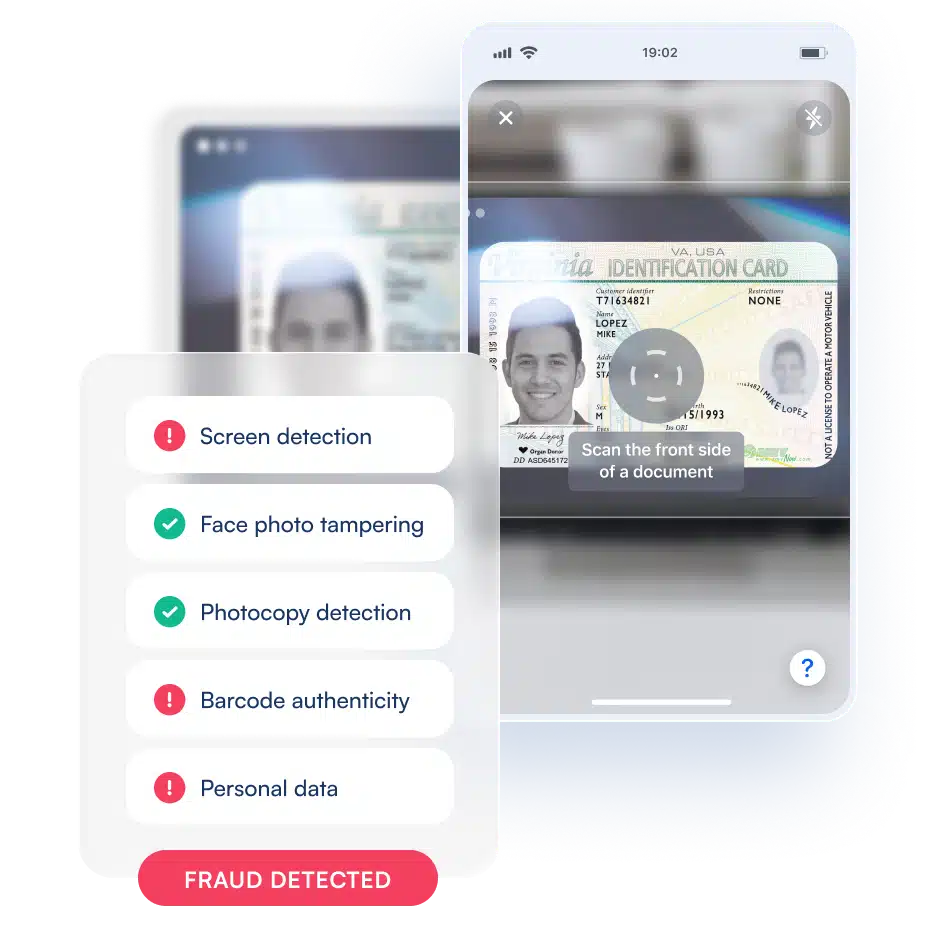
After data extraction comes the crucial verification phase. The system cross-references extracted data against authoritative databases and applies fraud detection logic to confirm the document is authentic and unaltered. This includes checks for:
- Document tampering or forgery indicators
- Consistency between machine-readable zones (MRZ) and visual inspection zones
- Expiration and validity status
- Watchlist and sanctions database screening (where applicable)
This step is critical for building trust and weeding out fraudulent activity before it reaches your platform.

Step 4: Result response
The final step—often overlooked in general descriptions but essential for technical evaluators—is the API’s result response. Once verification is complete, the API returns a structured output to your application. This typically includes:
- A pass/fail decision based on configurable thresholds
- A confidence score indicating the system’s certainty in the result
- Extracted data fields in a structured format (e.g., JSON)
- Flagged fields or risk indicators that may require additional review
- Error codes for cases where verification could not be completed
Your application then uses this response to determine the next step in the user journey—approving access, triggering a manual review queue, or declining the request.
Additional steps
Depending on your industry—whether it’s finance, healthcare, or eCommerce—there may be extra layers of verification to add. These could include KYC or AML checks, sanctions screening, or politically exposed persons (PEP) list lookups. A customizable verification API can incorporate these requirements effortlessly, ensuring you remain compliant without sacrificing efficiency or user experience.
Key features of an Identity Verification API
When evaluating identity verification APIs, it’s important to assess specific capabilities rather than treating all solutions as equivalent. Here are the key features to look for:
Document coverage and supported document types
A robust identity verification API should support a wide range of document types across a large number of countries, including:
- Passports (machine-readable and biometric)
- Driver’s licenses
- National identity cards
- Residence permits
- Visas and travel documents
Look for solutions that cover documents from 100+ countries and support multi-language document processing. Global coverage is especially important for businesses operating across borders or serving international user bases.
OCR accuracy and real-time processing speed
OCR accuracy directly affects how often verifications succeed on the first attempt. Higher accuracy rates reduce friction for legitimate users and lower the cost of manual review. Leading providers publish accuracy benchmarks—ask for these when evaluating vendors.
Real-time processing speed matters for user experience. Most API-based verifications complete in under 10 seconds end-to-end. Evaluate whether the provider’s infrastructure can maintain this performance at your expected verification volume.
Liveness detection and biometric facial matching
Liveness detection prevents spoofing attacks by confirming the user is physically present. Look for solutions that use active liveness challenges (e.g., head movement prompts) or passive liveness analysis (detecting depth and texture cues without requiring user action).
Biometric facial matching compares the selfie or live capture against the photo on the submitted document. Evaluate the false acceptance rate (FAR) and false rejection rate (FRR) to understand how the system balances security against user friction.
Confidence scoring and decision outputs
Rather than returning a simple binary result, leading APIs provide confidence scores that allow you to configure risk thresholds appropriate for your use case. For example:
- High-confidence matches can be auto-approved
- Mid-range scores can be routed to manual review
- Low-confidence results or flagged documents can be declined or escalated
This flexibility allows you to tune the verification workflow to match your risk tolerance and regulatory requirements.
Global database cross-referencing
The API should be able to cross-reference extracted identity data against authoritative global databases, including sanctions lists, PEP databases, and adverse media sources. This is particularly important for financial services organizations with AML obligations.
What are the three most common methods used to verify identity?
In the world of customer identity verification, three methods stand out for their efficacy and widespread use: Document Verification, Biometric Verification, and Knowledge-Based Verification. Each method has unique strengths, often working best when used in tandem.
Document Verification APIs
Document Verification APIs enable systems to confirm the authenticity of various global ID documents, including passports, driver’s licenses, and national IDs. These APIs automatically scan and extract information from identity documents, validate them, and return the results.
This method is often seen as the cornerstone of identity verification, especially for institutions that are highly regulated, such as:
- Online banking: To comply with KYC and AML regulations, online banks require rigorous ID verification.
- eCommerce: For high-value transactions, confirming the customer’s identity can prevent fraudulent activities.
- Healthcare: Ensuring the right individual is gaining access to medical records is critical for protecting patient data.
Biometric Verification APIs
Biometric verification has been rapidly adopted thanks to smartphone technology advances, which often include facial recognition and fingerprint scanners as standard features. Biometric Verification APIs capture and analyze unique biological traits of individuals—such as face, fingerprint, or voice—to securely verify their identity. This method adds an extra layer of security and is often used for quick yet secure mobile logins.
Integrating facial recognition and fingerprint sensors in smartphones has made biometric verification more accessible than ever. It’s a fast and frictionless way to verify user identities.
Knowledge-Based Verification APIs
Knowledge-based verification adds another layer of identity confirmation by asking users to answer questions that should be known only to them, like the name of their first pet or the street they grew up on. While effective, this method also raises security concerns because this kind of personal information can sometimes be guessed or unearthed through social engineering tactics.
Organizations that use this method must adhere to stringent data protection policies to ensure the user’s personal information remains confidential. For this reason, knowledge-based verification is typically used as a supplementary layer rather than a primary verification method.
Common use cases by industry
Identity Verification APIs serve a broad range of industries. Here are the most common deployment contexts:
Financial services and fintech
Banks, credit unions, neobanks, and fintech platforms use identity verification APIs to meet KYC and AML requirements during account opening, loan applications, and high-value transactions. Automated verification reduces onboarding time from days to minutes while maintaining regulatory compliance.
eCommerce and marketplaces
For high-value transactions or marketplace seller onboarding, identity verification prevents fraudulent accounts and chargebacks. According to a Statista report, eCommerce losses to online payment fraud were estimated at 41 billion U.S. dollars globally in 2022—much of which can be attributed to insufficient identity verification.
Healthcare
Healthcare providers use identity verification to confirm patient identity before granting access to medical records, telehealth services, or prescription management platforms. Accurate identity matching is also critical for insurance billing and fraud prevention.
HR and gig economy platforms
Staffing agencies, gig economy platforms (such as rideshare and delivery services), and remote-first employers use identity verification APIs during worker onboarding to confirm that applicants are who they claim to be. This is particularly important for roles involving access to sensitive environments, customer homes, or financial accounts. Automated verification speeds up the onboarding funnel while reducing the risk of fraudulent applications.
Gaming and age-restricted platforms
Online gaming platforms, gambling sites, and other age-restricted services use identity verification to enforce age requirements and comply with local regulations. Document verification APIs can confirm a user’s date of birth from a government-issued ID, while biometric matching ensures the person submitting the document is the same person attempting to access the platform.
Advantages of using an Identity Verification API
The integration of an ID Verification API offers advantages beyond the obvious benefit of accurate identification. These APIs are becoming essential tools for businesses prioritizing security, user experience, and compliance.
Enhancing online security
The first and foremost advantage is heightened online security. With real-time verification of IDs, you can ensure your users’ authenticity and proof of identification. By cross-referencing extracted information with authoritative databases, identity verification APIs act as an initial barrier to detect fraud, protecting businesses and end-users from harm.
Enhanced user experience
The customer journey is often laden with necessary but cumbersome verification steps that may discourage continued engagement. The easy integration of an ID Verification API streamlines this process, making it faster and more user-friendly for new customers. Automated verification that completes in seconds is significantly less disruptive than manual review processes that can take hours or days.
Ensuring KYC and AML compliance
Navigating the extensive regulations of KYC and AML is complex and can be resource-draining when handled manually. Identity Verification APIs are a game-changer in this context.
They automate multiple layers of verification checks, thereby streamlining compliance workflows. What used to take hours—or even days—can now be completed in a fraction of the time, with far less room for human error. The APIs can cross-reference identity documents against authoritative global databases, instantly flagging inconsistencies or potential risks. As a result, organizations, especially in heavily regulated sectors like financial services, can focus their human resources on more strategic tasks, confident their automated systems are maintaining compliance efficiently.
Impact on the bottom line
When it comes to the bottom line, every operational improvement has a ripple effect. Automating the identity verification process is no exception.
Firstly, it lowers the Customer Acquisition Cost (CAC). When the verification process is fast and smooth, more users are likely to complete their account setup, which means a lower spend per customer acquired.
Furthermore, an intuitive and quick verification process not only drives initial user engagement but also fosters long-term customer loyalty. People are more likely to return to platforms that offer a hassle-free experience.
These aren’t just user-centric advantages—they translate directly into increased revenue. By automating identity verification, businesses position themselves for scalability, better financial performance, and long-term growth.
How to integrate an Identity Verification API
For developers and technical evaluators, understanding the integration model is essential before committing to a solution. Here’s what to expect from a standard identity verification API integration.
REST API structure and authentication
Most identity verification APIs are built on REST architecture, using standard HTTP methods (POST, GET) and returning responses in JSON format. Authentication is typically handled via one of two methods:
- API keys: A static key passed in the request header, suitable for server-to-server integrations
- OAuth 2.0: Token-based authentication that supports more granular access control and is preferred for production environments handling sensitive data
Always transmit API keys and tokens over HTTPS and store them securely using environment variables or a secrets management service—never hardcode them in your application.
Available SDKs and supported platforms
Leading identity verification providers offer SDKs to simplify integration across common platforms and languages, including:
- Mobile: iOS (Swift/Objective-C) and Android (Kotlin/Java)
- Web: JavaScript/TypeScript SDKs for browser-based capture flows
- Backend: Libraries for Python, Node.js, Java, Ruby, and other server-side languages
SDKs handle the complexity of camera access, image capture optimization, and data transmission, reducing the amount of custom code your team needs to write.
Webhooks for real-time verification callbacks
For asynchronous verification workflows—where results may not be returned instantly—webhooks allow the verification service to push a result to your application as soon as processing is complete. This is particularly useful for:
- High-volume verification pipelines
- Workflows that include manual review steps
- Mobile applications where maintaining an open connection is impractical
Configure a webhook endpoint in your application to receive POST requests from the verification service, and implement signature verification to confirm that incoming webhook payloads are authentic.
Sandbox and testing environments
Before going live, use the provider’s sandbox environment to test your integration end-to-end without processing real identity documents. A well-designed sandbox should allow you to:
- Simulate successful verifications and failure scenarios
- Test error handling and edge cases
- Validate your webhook configuration
- Confirm that your application correctly parses and acts on different response types
Thorough sandbox testing reduces the risk of production issues and ensures your verification flow works correctly for all expected user paths.
Response formats and error handling
A standard API response will include a structured JSON object containing:
- Status field: Indicates whether the verification passed, failed, or requires review
- Confidence score: A numerical value (e.g., 0–100) representing the system’s certainty
- Extracted data: Structured fields such as name, date of birth, document number, and expiration date
- Risk flags: Specific indicators of potential fraud or document anomalies
- Error codes: Standardized codes for cases where verification could not be completed (e.g., image quality too low, unsupported document type)
Implement robust error handling in your application to manage all response types gracefully. For example, a low-quality image error should prompt the user to retake their photo rather than displaying a generic failure message.
Compliance and security considerations
For procurement teams and compliance officers, the security posture and regulatory alignment of an identity verification API provider are as important as the product’s features. Here’s what to evaluate.
GDPR and regional data privacy compliance
If you operate in the European Union or process data belonging to EU residents, your identity verification provider must comply with the General Data Protection Regulation (GDPR). Key requirements include:
- Data minimization: The provider should collect only the data necessary for verification
- Purpose limitation: Identity data should not be used for purposes beyond what the user consented to
- Data subject rights: The provider must support your ability to fulfill user requests for data access, correction, or deletion
- Data processing agreements (DPAs): Ensure a DPA is in place before processing any personal data through the API
Beyond GDPR, evaluate compliance with other regional frameworks relevant to your markets, such as CCPA (California), LGPD (Brazil), or PDPA (Thailand).
Security certifications
Look for providers that hold recognized security certifications, which demonstrate that their systems and processes have been independently audited:
- SOC 2 Type II: Confirms that the provider’s security controls are operating effectively over time, covering security, availability, processing integrity, confidentiality, and privacy
- ISO 27001: An internationally recognized standard for information security management systems
- PCI DSS: Relevant if the provider handles payment card data in conjunction with identity verification
Request copies of current certification reports during vendor evaluation.
Data retention policies and encryption standards
Understand exactly how long the provider retains identity data after a verification is complete, and whether you can configure retention periods to match your own data governance policies. Key questions to ask:
- Is biometric data (e.g., facial images) deleted after matching is complete?
- Is data encrypted at rest and in transit?
- What encryption standards are used (e.g., AES-256 for storage, TLS 1.2+ for transmission)?
- Where is data stored geographically, and does this align with your data residency requirements?
Audit trails and reporting
For regulatory review and internal compliance purposes, the provider should offer detailed audit logs that capture:
- Verification timestamps and outcomes
- Document types submitted
- Risk flags triggered
- Any manual review actions taken
These logs are essential for demonstrating compliance during regulatory audits and for investigating specific verification events after the fact. Confirm that logs are tamper-evident and retained for a period consistent with your regulatory obligations.
Advantages of using an Identity Verification API: summary
| Advantage | Impact |
|---|---|
| Fraud prevention | Real-time detection reduces financial losses and account takeover risk |
| Regulatory compliance | Automates KYC, AML, and regional privacy requirements |
| User experience | Faster onboarding reduces drop-off and increases conversion |
| Scalability | Handles verification volume spikes without additional headcount |
| Cost efficiency | Lowers per-verification cost compared to manual review |
| Auditability | Structured logs support regulatory review and internal governance |
Get started with identity verification
Identity Verification APIs are no longer optional infrastructure—they are a foundational requirement for any business that onboards users, processes transactions, or operates in a regulated industry. The right solution will balance security, user experience, compliance, and developer experience in a way that fits your specific use case.
When evaluating providers, prioritize:
- Document coverage and OCR accuracy for your target markets
- Liveness detection and biometric matching quality
- Compliance certifications and data privacy alignment
- Integration flexibility—REST API, SDKs, webhooks, and sandbox access
- Confidence scoring and configurable decision thresholds
- Audit trail and reporting capabilities
Get in touch today to speak with a Microblink identity expert and start your risk-free trial.