Account Takeover Fraud Statistics: The Latest ATO Data for 2026

Account takeovers (ATO) remain one of the most significant forms of identity fraud in 2026. In 2025, more than 6 million U.S. consumers experienced an ATO attack, which is an 18% increase from the previous year. Losses associated with account takeover exceeded $15 billion, making it the costliest individual fraud category tracked by Javelin Strategy & Research.
From credential attacks and bots to deepfakes and AI-assisted social engineering, the methods used to compromise digital identities continue to evolve. The following account takeover fraud statistics provide a snapshot of the scale of the problem in 2026, where attacks are occurring, and how businesses and consumers are being affected.
Key Account Takeover Fraud Statistics for 2026
The latest statistics show that ATO attacks are affecting millions of consumers while becoming part of a broader identity fraud ecosystem that spans account creation, authentication, transactions, and account recovery.
Among the most important statistics include:
- Microblink data shows that 30% of fraud failures involving U.S. identity documents were identified as fake documents, highlighting the role fraudulent credentials can play in establishing or gaining access to trusted accounts.
- In the U.S., photo forgery accounted for 60% of identity document fraud failures observed by Microblink, showing how frequently attackers manipulate legitimate documents rather than relying solely on completely fabricated credentials.
- Nearly 40,000 facility/account takeover cases were recorded during the first half of 2026, a 5% increase from H1 2025, according to UK fraud prevention organization Cifas.
- 5,100+ bank ATO complaints have produced more than $262M in reported losses since January 2025, according to the U.S. Department of Justice and FBI.
- 85% of usernames targeted in password-spray attacks had already appeared in known credential leaks, according to Microsoft.
- More than 97% of identity attacks observed by Microsoft were password attacks.
- 22,364 AI-related cybercrime complaints resulted in $893 million in reported losses in 2025, the first year the FBI tracked AI as a specific descriptor.
- 39% of contact center fraud calls were associated with account takeover attempts, according to Pindrop.
Taken together, these numbers illustrate why account takeover should no longer be viewed simply as a login security problem. An attack may begin with stolen credentials, but the consequences can extend through password recovery, payment changes, loyalty redemptions, high-value transfers, and other activity throughout the customer lifecycle.
Account Takeover Losses Continue to Increase
According to Javelin Strategy & Research’s 2026 Identity Fraud Study, account takeover remained the single costliest fraud category it tracked. Approximately 6 million U.S. consumers experienced ATO during 2025, an 18% increase from 2024.
That creates an interesting divergence in the data: more people are experiencing account takeovers, even though the aggregate financial losses associated with those attacks have declined slightly.
The trend becomes even clearer when viewed against the broader identity fraud landscape. Javelin estimated total U.S. identity fraud losses, excluding scams, at $27.3 billion in 2025, essentially unchanged from $27.2 billion the previous year. Approximately 18 million people were affected.
New-account fraud moved in the opposite direction. Losses increased to approximately $7 billion, while the number of victims rose 31% to 5.4 million, Javelin found.
That matters because new-account fraud and account takeover are different manifestations of the same underlying identity problem. In one scenario, a fraudster uses stolen or synthetic identity information to establish a new account. In the other, an attacker compromises an identity that a business has already learned to trust.
The FBI’s broader cybercrime data provides additional context. The FBI Internet Crime Complaint Center recorded $20.877 billion in reported cybercrime losses during 2025, up 26% year over year, across more than 1 million complaints. Identity theft complaints increased 48%, from 21,403 in 2024 to 31,675 in 2025.
The FBI does not maintain a dedicated account takeover category, so its identity theft and personal data breach figures should not be treated as direct measures of ATO. They nevertheless illustrate the scale of the identity and credential ecosystem that helps enable account compromise.
Account Takeover Has Increased Dramatically Over the Past Five Years
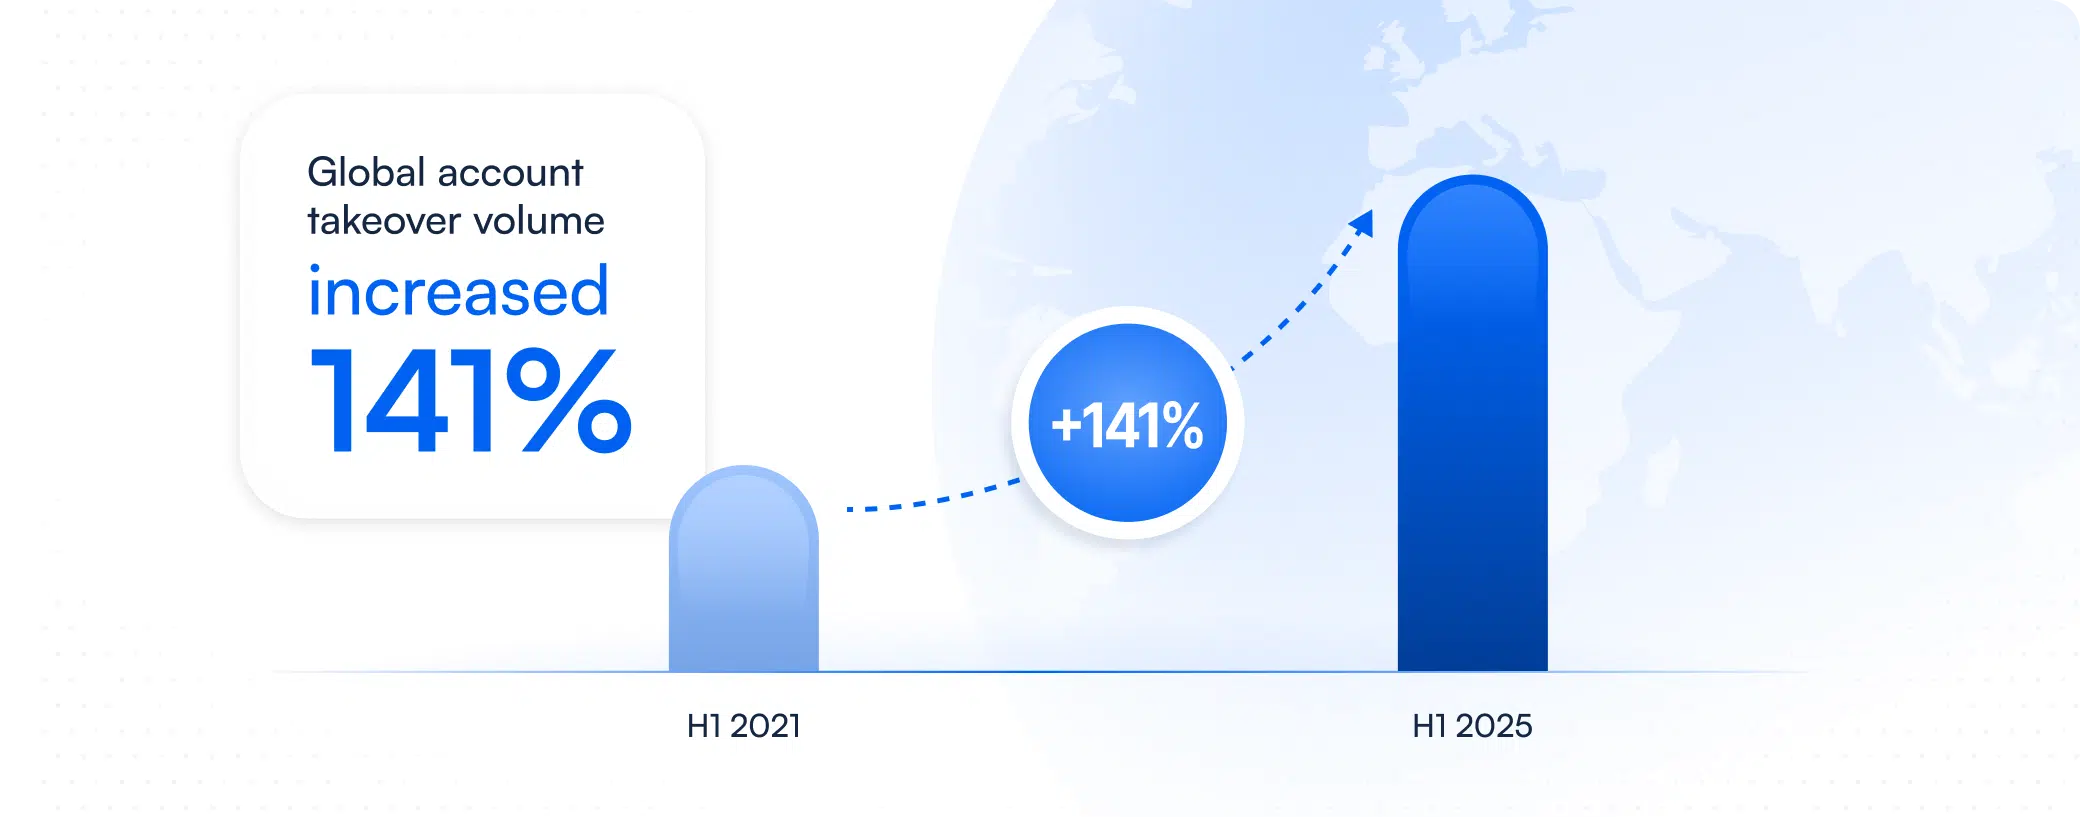
While loss estimates provide one way to understand ATO, fraud network telemetry provides another. TransUnion reported a 21% increase in global digital account takeover volume between H1 2024 and H1 2025, extending a much longer pattern of growth.
Attackers are also targeting different stages of the customer journey. TransUnion found that 8.3% of global digital account creation attempts were suspected of fraud in 2025, making account creation the riskiest stage of the consumer lifecycle. That represented an 18% year-over-year increase.
The significance of these numbers extends beyond account opening. Fraudsters who successfully create accounts using stolen or manipulated identities can establish accounts that appear legitimate before using them for later fraudulent activity. Conversely, legitimate accounts that have already passed identity checks can become targets for takeover months or years later.
This creates a challenge for fraud prevention systems built around a single point in time. An identity that was legitimate when an account was created does not guarantee that the person controlling that account today is the same person.
Bots and Automated Attacks Are Increasing the Scale of Identity Fraud
Automation has fundamentally changed the economics of account takeover. Instead of manually testing individual usernames and passwords, attackers can use automated tools to test enormous numbers of credentials, identify active accounts and concentrate their efforts on successful combinations.
A Cloudflare report found that as of May 2026, 57.4% of all web activity came from AI agents and bots compared to just 42.7% being driven by humans
Login traffic provides another window into the problem. F5 Labs found that 10.6% of web authentication traffic and 5.2% of mobile API authentication traffic was malicious, even in environments where bot mitigation was already deployed.
These attacks are particularly important for account takeover because automation allows criminals to operate at a scale that would be impossible manually. A single leaked credential database can be tested against numerous services, exploiting the tendency of consumers to reuse usernames and passwords across different accounts.
More Than 97% of Identity Attacks Are Password Attacks
Password spray and other large-scale password attacks accounted for more than 97% of identity attacks observed by Microsoft.
Microsoft reported that identity-based attacks increased 32% during the first half of 2025, with password attacks representing more than 97% of the total. Microsoft also found that 85% of usernames targeted by password-spray attacks had already appeared in known credential leaks.
The concentration of attack infrastructure is striking as well. Just 20 autonomous system numbers, representing approximately 0.04% of networks, were responsible for more than 80% of malicious password-spray traffic measured by Microsoft.
Multifactor authentication remains one of the strongest defenses against credential attacks. Microsoft has reported that MFA can block more than 99% of identity attacks. But MFA should not be viewed as the end of the identity security process.
Attackers increasingly target pathways that exist around authentication, including account recovery, session theft, social engineering and changes to trusted account information. A criminal who gains control of an authenticated session does not necessarily need to defeat the original login process again.
This is why account takeover prevention increasingly requires organizations to evaluate identity throughout the account lifecycle rather than treating successful authentication as permanent evidence of trust.
ATOs Target More Than Just Financial Accounts
Of course, a bank account or other financial account is the dream target for fraudsters launching ATO attacks. However, any account linked to a payment device or store of value is also a prime target. A compromised food delivery account may contain payment credentials. A gaming account can contain valuable digital goods. A loyalty account can hold points that can be transferred or redeemed. Ticketing and subscription accounts can have resale value, while social media accounts can provide an established identity that can be exploited for scams or further social engineering.
This broadening attack surface also means organizations outside financial services increasingly need to think about account takeover as an identity problem.
Accounts Involving Money Remain a Major Target for ATO
The attraction is straightforward: financial accounts provide attackers with a direct path to monetary value.
TransUnion’s broader fraud data similarly found significant risk outside financial services. Among U.S. transactions in 2025, suspected digital fraud rates reached 11.7% in online communities such as dating sites and forums and 9.8% in gaming.
The takeaway is that any account containing money, payment credentials, personal information, reputation, digital assets, access privileges or accumulated value can become attractive to an attacker.
AI and Deepfakes Are Changing Account Takeover Attacks
Account takeover has traditionally been associated with stolen passwords and credential stuffing, but generative AI is expanding the tools available to attackers.
Deepfakes can be used in attempts to impersonate legitimate customers during identity checks. Generative AI can improve phishing and social engineering content. Automated systems can help criminals execute attacks at greater scale, while injection techniques can introduce manipulated media directly into verification workflows.
Deepfakes represented one in five biometric fraud attempts, with deepfaked selfies increasing 58% and injection attacks increasing 40% year over year.
Pindrop’s research into contact center fraud provides another example. Account takeover accounted for 39% of fraud calls, including attempts involving credential resets, changes to personally identifiable information and reinstatement of restricted accounts. Pindrop also reported a 1,300% increase in the rate of deepfake attacks over one year, from approximately one every two days to seven per day.
Meanwhile, the FBI recorded 22,364 complaints containing its new AI descriptor in 2025, representing approximately $893 million in reported losses.
AI does not replace traditional account takeover techniques. Instead, it can make different stages of an attack more scalable and convincing, combining credential theft, impersonation, social engineering and automated activity into increasingly complex attack chains.
Account Takeover Is Increasingly a Multi-Step Attack
Identity theft complaints to the FBI increased 48% in 2025, rising from 21,403 to 31,675 complaints and accounting for $185.8 million in reported losses.
This is one of the most important changes in how organizations should think about account takeover.
Fraud does not necessarily begin and end with a malicious login. An attacker may obtain credentials through phishing or an infostealer, access an existing account, change information associated with that account, establish new payment details and then wait before attempting to extract value.
The individual actions may appear legitimate when viewed independently.
That makes context increasingly important. A successful password followed by a device change may not necessarily indicate fraud. Neither may an address change or a high-value transaction. But several unusual signals appearing together can tell a very different story.
Account takeover detection therefore increasingly depends on connecting signals across an entire interaction rather than asking whether any individual event looks fraudulent in isolation.
MFA Is Essential, but Identity Verification Cannot End at Login
MFA can stop more than 99% of identity attacks, but attackers can still target recovery processes, authenticated sessions and activity occurring after login, according to Cybersecurity firm Nexus Grid Limited.
The continued effectiveness of MFA should not be understated. For credential-based attacks, it remains one of the most valuable security controls available. The challenge is that account takeover is broader than credential theft.
Once a user has successfully authenticated, businesses continue making implicit trust decisions throughout the relationship. Those moments can require different levels of assurance.
Rather than subjecting every customer to maximum friction during every interaction, organizations can introduce step-up verification when risk changes. Identity document verification, biometrics, device intelligence, behavioral signals and transaction context can provide additional evidence when an interaction warrants greater scrutiny.
The objective is not to verify customers repeatedly for the sake of verification. It is to establish the appropriate level of trust for the action being performed.
Consumers Are Willing to Accept More Verification When the Risk Justifies It
One in six U.S. consumers reported losing money to digital fraud in the previous year, with a median loss of $2,307, according to TransUnion.
Fraud teams have traditionally faced a difficult tradeoff. Stronger controls can reduce fraud, but excessive friction can frustrate legitimate customers and lower conversion.
The latest data suggests consumers are more receptive to additional security when they understand why it is being used.
Consumers value stronger protection, but how that protection is applied matters. In a 2026 global survey from TarnsUnion, 77% of consumers said confidence that their personal data is secure was the most important factor when choosing whom to transact with online. At the same time, unnecessary intervention can carry a measurable cost. Research from Datos Insights found that 44% of surveyed e-commerce merchants had false-decline rates above 3%, while only 12% believed their rates were that high. Research from media organization PYMNTS.com found that 47% of merchants say false declines have cost them sales.
The challenge is therefore not choosing between security and customer experience. It is determining when additional friction is justified.
Risk-based identity verification can allow low-risk users to continue with minimal interruption while triggering stronger verification when account behavior, transaction characteristics, device signals or other evidence indicates elevated risk.
Account Takeover Can Permanently Damage Customer Trust
According to TransUnion, U.S. companies reported losing an average 9.8% of annual revenue to fraud, while surveyed businesses globally reported average losses of 7.7%
The financial impact of account takeover, however, does not end when fraudulent transactions are reimbursed. The impact of account takeover can continue long after the initial compromise. Javelin Strategy & Research found that ATO victims spent an average of 17 hours resolving fraud in 2025, significantly higher than the 10.4-hour average across identity fraud victims overall.
How organizations respond can also influence the longer-term customer relationship. Research published by the American Bankers Association found that 69.9% of consumers said the way their financial institution handled fraud resolution had a greater impact on their trust than discovering the fraud itself. Another 72.1% said a fraud experience affected their confidence in the institution’s other services.
Those statistics turn account takeover from a fraud-loss calculation into a customer-retention issue.
Consumers entrust organizations with their identity information, payment credentials and account data. When that trust is compromised, the quality and speed of the response can determine whether the relationship survives.
Why Account Takeover Requires Continuous Identity Intelligence
Account takeover exposes a fundamental weakness in traditional approaches to digital identity: trust changes over time.
A legitimate person may create an account and successfully pass identity verification. The same person may later enable MFA and use that account safely for years. None of those events guarantees that every future interaction with the account is legitimate.
Modern fraud attacks move across the customer journey. They adapt and target the moments where trust is assumed rather than verified.
That is why identity decisions increasingly need to incorporate multiple layers of evidence. Documents and biometrics can establish identity, while device, behavioral and transactional signals can provide context around how that identity is being used. Higher-risk moments can then trigger additional verification rather than forcing every customer through the same process.
At Microblink, we describe this broader approach as Know Your Actor: understanding who or what is behind an interaction and continually evaluating whether the available evidence supports the action being attempted.
This is particularly important as AI agents become more common. Digital interactions will increasingly involve not only humans, but software acting on their behalf. Establishing identity at account creation will remain important, but organizations will also need to understand who is acting, under whose authority, and whether the behavior makes sense within the context of the relationship.
The Account Takeover Statistics to Watch in 2026 and Beyond
The latest data does not point to the disappearance of account takeover. It points to its evolution.
Losses can decline while victim counts rise. Authentication defenses can improve while attackers shift toward account recovery or authenticated sessions. Fraud rates can decline in aggregate while specific industries, account types or stages of the customer journey become more heavily targeted.
That is why no single statistic provides a complete picture of ATO.
The clearest trend across the 2025 and 2026 data is that identity fraud is becoming more interconnected. Credential attacks, automated bots, synthetic identities, deepfakes, social engineering and account takeover increasingly overlap rather than functioning as separate categories.
For organizations, the implication is equally clear. Identity cannot be treated as something established once at onboarding and then trusted indefinitely. As attackers become more adaptive, organizations need the ability to establish and re-establish trust throughout the customer lifecycle.