Echa un vistazo a las entradas del blog repletas de información sobre el sector.
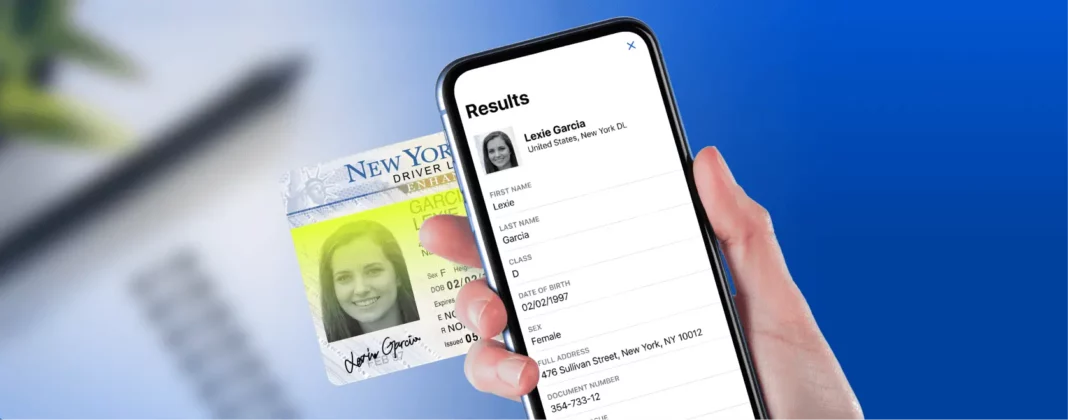
Document fraud has evolved far beyond blurry photocopies and obvious forgeries. Today’s attackers use high-quality templates...

Fraud has outgrown rules engines and manual review queues. Synthetic identities, stolen credentials, and automated attacks no...
Digital onboarding is the defining moment for users who engage with modern banking and financial products. The first interact...

As businesses scale in an increasingly digital economy, the stakes for secure and efficient transaction processing have never...
As financial technology continues to expand, the sophistication of digital fraud has grown right alongside it, making robust...
For fraud decision-makers in banking, AML software selection is no longer just a compliance exercise. In 2026, it is a strate...
Payment fraud is no longer confined to stolen cards and simple rule evasion. Today’s attacks blend synthetic identities, auto...

Designing a retail banking customer onboarding process has never been more difficult, or more critical. Product managers must...
As financial crimes become increasingly sophisticated in 2026, banks and financial institutions must adopt advanced technolog...

In 2026, digital onboarding is no longer just a customer experience initiative. For banks, it is a core control point for fra...

As banks move deeper into 2026, AML decision-making is becoming less about buying a single compliance tool and more about bui...
Navigating the digital commerce landscape in 2026 requires a strategic balance between ironclad security and a frictionless u...
Explorar nuestras soluciones está a un clic de distancia. Prueba nuestros productos o habla con nosotros con uno de nuestros expertos para profundizar en lo que ofrecemos.

La IA no solo ha acelerado el fraude, sino que lo ha convertido en un sistema. Hemos analizado millones de interacciones relacionadas con la identidad para trazar un mapa de cómo están evolucionando los ataques a la identidad en las distintas regiones, según los tipos de ataque y los niveles de sofisticación, y qué deben replantearse las organizaciones para mantenerse al día.
Ver los datos